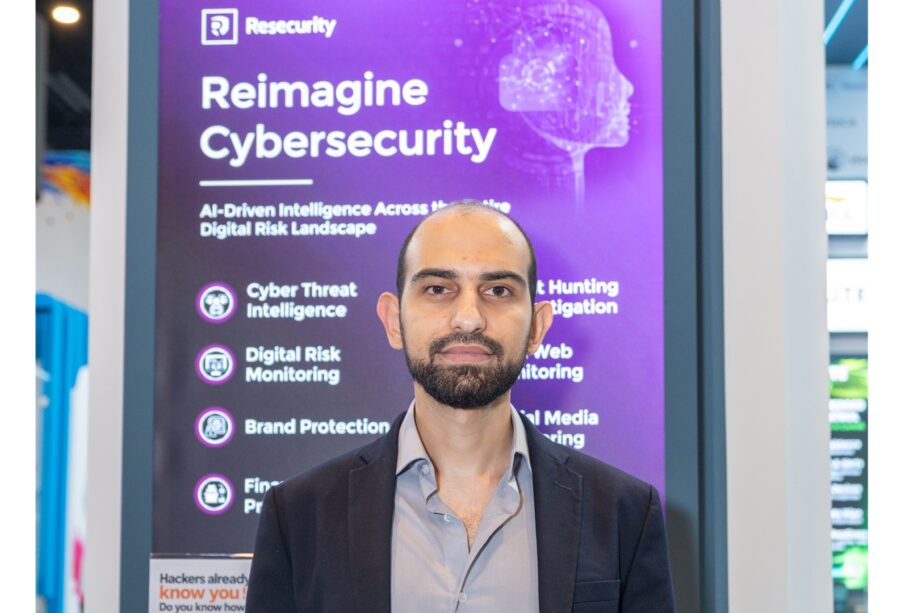
Ahmad Halabi. Managing Director, Resecurity
Ahmad Halabi, Managing Director at Resecurity, discusses the evolving cyber threat landscape, the company’s offensive security expertise, AI-powered Cyber Fusion Center, threat intelligence capabilities and approach to protecting organisations, brands and individuals against emerging cyber risks.
How is the threat landscape evolving with the emergence of AI-driven threats and agentic AI, and how are your solutions adapting?
It’s all about the background we come from. We are experts in understanding hackers’ mentality, mindset, their way of thinking, their approach, techniques and motivations.
We’ve been in the ethical hacking industry for a long time, identifying vulnerabilities and zero-days, much like cybercriminals do, but from an ethical perspective. This makes it easier for us to develop solutions that can counter what hackers do. Essentially, we use offensive techniques for defensive purposes. We map advanced threats and the activities of threat actors to ensure that we’re combating them effectively and providing end users with solutions that address their security needs as threats continue to evolve.
Can you elaborate on your AI-powered cyber fusion centre and how it helps organisations respond to emerging threats?
We have a fusion centre where we bring together data acquired from various sources, including the dark web, social media and other intelligence sources. We use AI to normalise and structure this data, ensuring that customers receive the intelligence they need to secure their environments faster.
The objective is to provide customers with information that is relevant and valuable to them, so they can take immediate action before a threat materialises.
Beyond enterprise security, you also offer identity protection for individuals. What does this involve, and who are your customers?
If you’re a VIP or an executive concerned about protecting your identity, we can help you understand who might be trying to impersonate or attack you. We monitor your identity online to identify whether your passwords have been leaked, whether someone is impersonating you on social media, or whether there are attempts to attack or blackmail you. We can monitor and identify these activities and even prevent further harm by taking down suspicious or malicious content.
We offer both brand protection and individual VIP and executive protection. We have a global presence, and our customers include football players, well-known athletes, government officials and other high-profile individuals.
What are your key areas of focus in helping organisations protect their data and digital assets?
Everything we do is centred around data, how you store it, how you secure it and how you ensure that it doesn’t get leaked. If a leak does occur, it’s about understanding how to contain it and minimise the damage to your company and brand. Our capabilities cover threat intelligence, fraud prevention, brand protection, identity protection and the identification of vulnerabilities and zero-days. The objective is to help organisations understand the threats they face and protect themselves against potential financial and reputational damage.
Threat detection is important, but how do you help organisations take action once a threat has been identified?
Whatever we detect, we can integrate with the customer’s existing tools and environments. For example, if we detect malware behaviour, we can integrate that intelligence with their EDR platform. If we identify indicators of compromise (IOCs), we can integrate them with their SIEM so that appropriate action can be taken. Similarly, if we identify a vulnerability, we can integrate that information with a vulnerability management tool.
Everything we detect can be integrated with a solution that helps the customer address the issue immediately. We also have products that can help fix these issues. For example, if we detect impersonation, we can remove the malicious content from the internet. If we identify malware activity, we can guide customers on how to remove the malware from their networks.
So we’re not just detecting threats. We’re also helping customers address and fix them, while ensuring that lessons are learned to prevent similar incidents in the future.
Do you also offer managed services for organisations that may not have the resources to manage these security platforms internally?
Yes, we offer managed services as well. If a customer doesn’t have sufficient resources to manage the platform or handle the specific security areas we cover, our team can take care of everything on their behalf. This allows customers to focus on the business side of things while we concentrate on their security requirements.
What role does your Context platform play in your threat intelligence portfolio?
Context is our threat intelligence platform. It supports threat feeds, threat acquisition, threat hunting and various threat intelligence operations. It helps organisations access and work with the intelligence they need to understand and address emerging threats.
What have been the major product advancements over the past six months, particularly in AI?
We’ve developed a number of use cases using our own AI capabilities. One of the key areas is helping customers better understand the intelligence information we identify. AI allows us to simplify that information and guide users through the steps required to address an issue.
Rather than presenting complex intelligence that customers must interpret themselves, we can provide specific, easy-to-understand, step-by-step guidance on how to fix the problem.
Can you explain the capabilities of your endpoint protection platform and how it fits into your wider security portfolio?
We provide our Endpoint Protection Platform to customers as part of a comprehensive cybersecurity offering. It doesn’t function only as an endpoint protection solution. It also provides insider threat monitoring capabilities. For example, if an organisation wants to identify whether an insider is leaking information, the platform can help monitor that activity. There is also an agent installed on the endpoint that can identify attacks and take action to remove threats. The agent can detect malware, isolate or quarantine threats, and acquire indicators of compromise for further investigation. As organisations operate across increasingly distributed environments, including cloud and on-premises infrastructure, the platform is designed to support different operating systems.
Elaborate on your partnership with Bulwark Technologies?
Bulwark Technologies is our distributor in the region. They help us distribute our platforms to the right audience and reach companies that have a need for these products. The partnership helps us connect our solutions with organisations looking to strengthen their cybersecurity capabilities.
Finally, what would be your key message to organisations looking to strengthen their cyber resilience?
If you want to protect your brand and identify anything that could harm your business or lead to financial loss, we’re here to support you. Our focus is on helping organisations identify threats, protect their information and take the necessary action to minimise potential damage

Leave a reply