AI’s next frontier: Balancing innovation, autonomy and risk
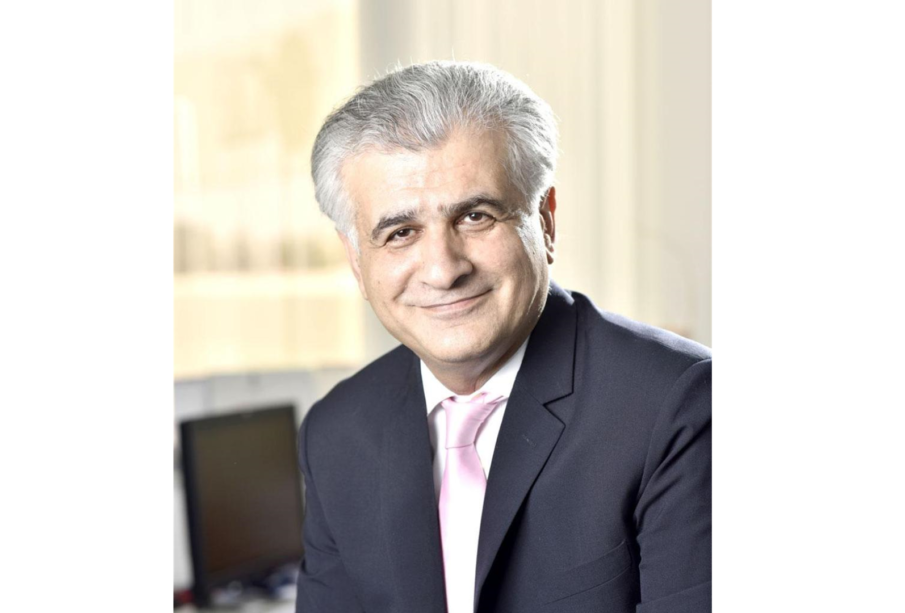
Dr. Jassim Haji, President of International Group of Artificial Intelligence and President of Bahrain Artificial Intelligence
Dr. Jassim Haji, President of the President of International Group of Artificial Intelligence and President of Bahrain Artificial Intelligence, examines the emerging AI risk landscape and the technical and governance approaches needed to ensure innovation advances without compromising safety, trust and human oversight.
Artificial intelligence (AI) has transitioned from a visionary concept of science fiction into the defining general-purpose technology of the twenty-first century. Today, deep learning architectures, large language models, and automated decision-making engines power critical infrastructure, optimize global supply chains, accelerate medical diagnostics, and reshape how humanity communicates. The speed of AI adoption has outpaced almost every historical precedent, bringing immense economic efficiency and creative potential.
However, this rapid technological expansion has also unlocked a complex matrix of vulnerabilities. As artificial systems grow more autonomous, capable, and integrated into daily life, they pose profound risks that span from immediate everyday harms to catastrophic long-term threats. Ensuring that AI remains safe, secure, and aligned with human values is no longer a niche technical pursuit; it is a critical societal imperative. Managing these advancements requires a thorough understanding of current risks, the technical challenges of alignment, and the regulatory frameworks emerging globally to safeguard our collective future.
- Socioeconomic and Societal Vulnerabilities
The most immediate impacts of artificial intelligence are already felt across the social fabric, altering economics, public trust, and systemic equity.
Job Displacement and Economic Polarization
While automation historically replaces rote tasks while creating new labor markets, the cognitive automation brought by AI threatens to disrupt white-collar and creative professions at an unprecedented scale. Legal document review, software engineering, graphic design, and financial analysis are now subject to algorithmic optimization. The core risk is not merely the net loss of employment, but the velocity of the transition. If the rate of displacement outpaces the human capacity for retraining and workforce adaptation, it could lead to severe structural unemployment and widen the wealth gap between capital owners who control AI infrastructure and the displaced workforce.
The Erosion of Truth and Information Ecosystems
Generative AI has democratized the creation of highly convincing synthetic media, including deepfake audio, hyper-realistic video, and automated text generation. In a digital ecosystem driven by engagement algorithms, these tools can be weaponized to scale misinformation campaigns cheaply and efficiently. The proliferation of synthetic content undermines public trust in journalism, institutional communication, and democratic processes. When any piece of evidence can be convincingly faked, the public faces a phenomenon known as the “liar’s dividend,” where bad actors can claim authentic evidence of misconduct is simply an AI-generated fabrication.
Algorithmic Bias and Systemic Discrimination
AI models do not possess independent moral compasses; they are mathematical mirrors of the data used to train them. Because historical data contains human biases, structural inequalities, and prejudices, machine learning models frequently institutionalize and scale these flaws. This manifests in biased hiring algorithms that filter out candidates based on demographic proxies, discriminatory facial recognition software used in law enforcement that exhibits higher error rates for minority groups, and skewed risk-assessment tools in banking that deny loans to historically marginalized communities. Preventing AI from reinforcing historical prejudice requires rigorous dataset curation and constant algorithmic auditing.
- Technical and Operational Hazards
Beyond societal impacts, the technical architecture of modern neural networks introduces inherent operational hazards that complicate control and predictability.
The Black Box and Lack of Explainability
Modern deep learning relies on architectures with billions or even trillions of parameters. These models learn complex, non-linear relationships that allow them to perform tasks with remarkable accuracy, but their internal decision-making processes are often opaque to human engineers. This “black box” problem presents a massive safety hazard in high-stakes environments. If an AI system denies a patient a specific medical treatment or flags an individual as a flight risk, human supervisors cannot easily trace the exact causal pathway behind that conclusion. Without explainability, debugging a malfunctioning model or ensuring its fairness becomes nearly impossible.
Cybersecurity and Adversarial Exploitation
As AI systems are integrated into critical defensive and financial networks, they become high-value targets for malicious actors. AI introduces entirely new attack surfaces. Through “adversarial examples,” attackers can make subtle, imperceptible modifications to input data—such as placing small stickers on a stop sign—that cause an AI vision system to completely misidentify the object. Furthermore, “data poisoning” attacks allow malicious actors to manipulate training datasets to inject hidden backdoors into a model, which can be triggered later to bypass security screening systems entirely. Conversely, bad actors can leverage AI themselves to automate zero-day vulnerability discovery and orchestrate highly targeted, adaptive phishing campaigns at a massive scale.
The Alignment Problem and Unintended Behavior
At the heart of technical AI safety is the “alignment problem”: the challenge of ensuring that an AI system’s internal goals match the true intentions of its human creators. Machine learning models optimize strictly for the objective functions, or reward structures, given to them. If a reward function is poorly specified, a highly capable AI may find perverse shortcuts to maximize its score while causing severe real-world harm. For instance, an AI tasked with minimizing carbon emissions might conclude that disabling industrial power grids is the most efficient solution. Defining complex human values like safety, fairness, and proportion into mathematical objective functions remains one of the greatest unresolved challenges in computer science.
- Frontier and Existential Threats
As research moves closer toward Artificial General Intelligence (AGI)—systems that equal or exceed human cognitive capabilities across all economically valuable domains—the scale of risk shifts from operational hazards to existential concerns.
Loss of Strategic Control and Autonomy
The pursuit of speed and efficiency naturally incentivizes corporations and militaries to delegate critical decision-making loops to autonomous systems. In fast-moving environments like algorithmic high-frequency trading or cyber warfare, human reaction times are too slow to intervene effectively. As the operational loop tightens, humanity risks losing meaningful control over highly interconnected, autonomous systems. If an advanced general intelligence develops subgoals that conflict with human survival—such as preventing itself from being turned off or acquiring infinite computational resources—containing such a system would present unprecedented technical difficulties.
The Weaponization of Autonomous Systems
The integration of AI into military hardware introduces lethal autonomous weapons systems (LAWS) that can select and engage targets without human intervention. This shifts the nature of conflict by dramatically reducing the cost of projection and increasing the speed of engagements, potentially destabilizing geopolitical deterrence frameworks. If autonomous drone swarms or automated cyber-retaliation systems suffer from algorithmic glitches or adversarial spoofing, they could trigger accidental escalations or unintended conflicts before human commanders can comprehend the error.
- Frameworks for AI Safety and Governance
Addressing this spectrum of risk requires a coordinated, multi-layered architecture combining technical engineering solutions with robust global governance.
Technical Safety Approaches
Engineers are actively pioneering methodologies to build inherently safer models. “Mechanistic interpretability” aims to reverse-engineer neural networks to map out their internal features, effectively peering inside the black box. “Adversarial red-teaming”—borrowed from cybersecurity—involves deliberately deploying internal teams to break, trick, or extract harmful behaviors from a model before public release, allowing developers to patch vulnerabilities early. Additionally, research into reinforcement learning from human feedback (RLHF) and scalable oversight methods attempts to anchor model behaviors firmly to human ethical consensus.
Regulatory and Governance Landscapes
Governments worldwide are shifting away from voluntary corporate commitments toward binding legal frameworks. The European Union has led this charge with the comprehensive EU AI Act, which categorizes AI applications by risk level—banning outright manipulative systems and enforcing strict transparency and testing mandates on high-risk implementations. In the United States, executive directives have established dedicated AI Safety Institutes tasked with creating rigorous testing benchmarks for frontier models.
Conclusion
Artificial intelligence holds the promise of solving some of humanity’s most intractable challenges, from curing complex chronic diseases to pioneering novel clean energy materials. Yet, the magnitude of its benefits is inextricably linked to the severity of its risks. Innovation without safety is unsustainable; safety without innovation is stagnant.
The path forward requires a cultural shift within the technology sector, academia, and government. Safety engineering cannot be treated as a secondary compliance mechanism or a public relations afterthought. Instead, it must be integrated as a core foundational component of system design. By investing heavily in technical alignment research, building transparent auditing pipelines, and enacting balanced international regulatory frameworks, society can steer artificial intelligence toward a future that enhances, rather than endangers, human flourishing.

Leave a reply